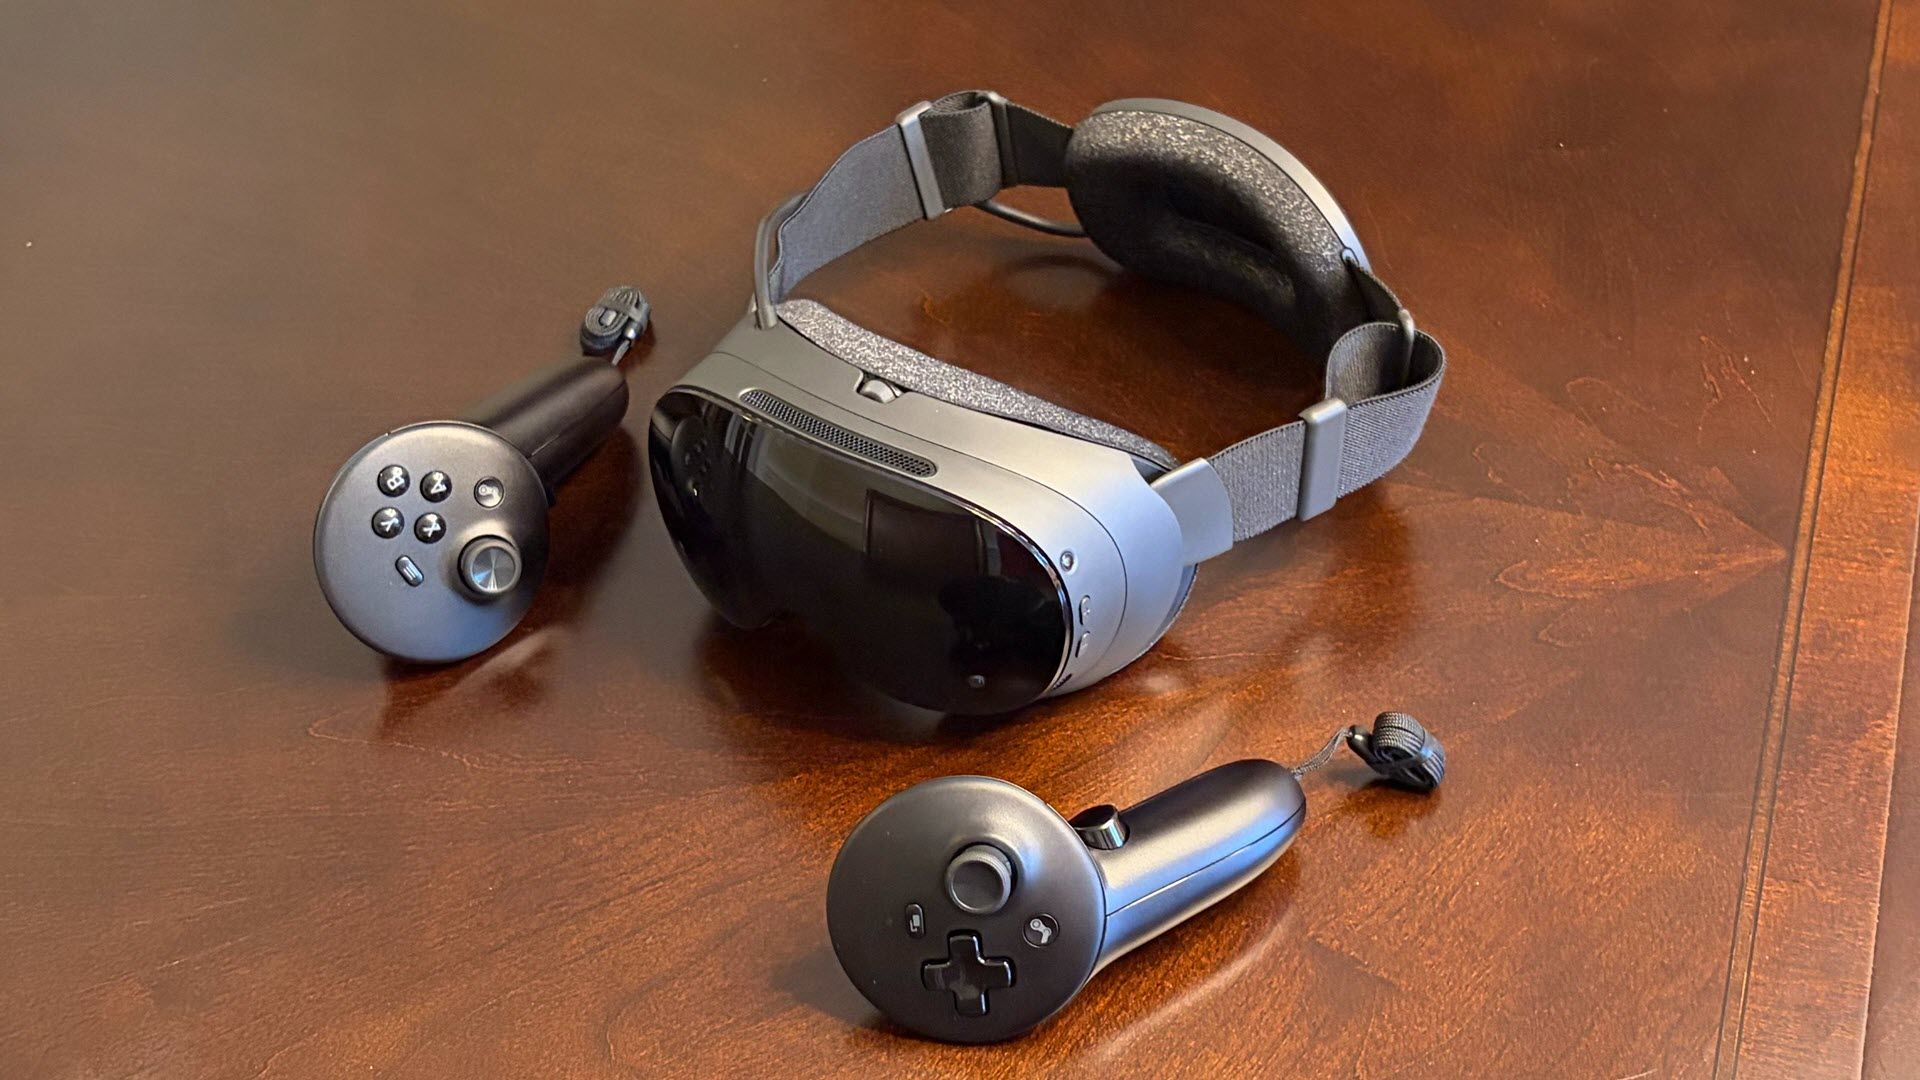
alessandro@lemmy.ca to PC Gaming@lemmy.caEnglish · 3 days agoValve adds CD-ROM drive support to Steam Frame kernel, took less than ten minutes — update comes one day after user requests for capability in the Steam Community forumwww.tomshardware.comexternal-linkmessage-square84linkfedilinkarrow-up1521arrow-down12
arrow-up1519arrow-down1external-linkValve adds CD-ROM drive support to Steam Frame kernel, took less than ten minutes — update comes one day after user requests for capability in the Steam Community forumwww.tomshardware.comalessandro@lemmy.ca to PC Gaming@lemmy.caEnglish · 3 days agomessage-square84linkfedilink
minus-squareklankin@piefed.calinkfedilinkEnglisharrow-up12arrow-down1·3 days agoThats a really good point, especially with the more obscure modules. It must be interesting for steam to develop a hackable device in a market that usually locks their hardware down so aggressively.
minus-squareTruscape@lemmy.blahaj.zonelinkfedilinkEnglisharrow-up6·edit-23 days agoI mean just because steam doesn’t mind you tinkering with their own hardware doesn’t mean they should not try to secure the base system OS against outside intrusion (like a RAT entering in via an AUR installation using modules as an entry point)
minus-squareklankin@piefed.calinkfedilinkEnglisharrow-up2·3 days agoYeah, sorry I meant more in the way that a user in a VM is a really different threat surface to a full root user. For sure both should apply security patches, and avoid malware, I’m just wondering even within that model what the differences are.
Thats a really good point, especially with the more obscure modules.
It must be interesting for steam to develop a hackable device in a market that usually locks their hardware down so aggressively.
I mean just because steam doesn’t mind you tinkering with their own hardware doesn’t mean they should not try to secure the base system OS against outside intrusion (like a RAT entering in via an AUR installation using modules as an entry point)
Yeah, sorry I meant more in the way that a user in a VM is a really different threat surface to a full root user.
For sure both should apply security patches, and avoid malware, I’m just wondering even within that model what the differences are.